SHA-256 Incident Fingerprinting & Dedup Engine — F
By (author)Sehreen Atta Gul
read more
Read Me
SHA-256 Incident Fingerprinting & Dedup Engine — Fixly
What it does
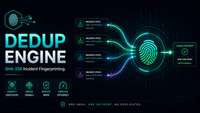
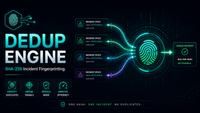
Prevents alert fatigue by recognizing when a new error log line is actually the same underlying failure as one already being tracked — rather than creating a fresh incident every single time.
How it works
1. Normalizes the error message and type into a canonical string (strips out variable data like timestamps, IDs, and stack line numbers).
2. Generates a SHA-256 hash fingerprint from that normalized string.
3. Checks if an open incident already exists with the same fingerprint.
4. If it exists: increments the occurrence counter and updates last-seen timestamp.
5. If it's new: creates a fresh incident and broadcasts it live to the dashboard.
Why it matters
Without deduplication, a single recurring bug firing every few seconds would flood a dashboard with thousands of duplicate incidents, making it impossible for an engineer — or an AI — to see the real signal. This engine collapses repeated noise into one trackable incident with an accurate occurrence count.